

Trump Mobile Hackers Claim the Company Admitted It Had 'No Team' To Handle the Data Breach
Two little-known gangs have breached the presidential-branded telecom in a matter of weeks
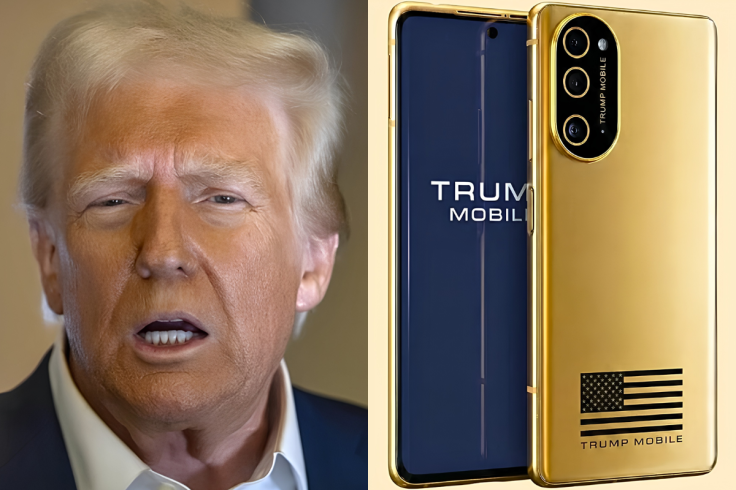
Hackers who say they stole data from 3,615 Trump Mobile customers this week claim the company shrugged off their warning by admitting it had 'no team' to handle the breach, potentially exposing names, emails, and home addresses online.
The group, which calls itself BYOD, posted the records on a dark web leak site and said Trump Mobile branded anyone who hacks it a terrorist. Straight Arrow News reported the leak first, and PCMag and Cybernews said sample records appeared genuine. Trump Mobile has not confirmed the breach or the alleged response.
Trump Mobile uses the Trump brand under licence and is operated by T1 Mobile, with the venture promoted by Eric Trump and Donald Trump Jr. That political wrapper turns a telecom breach into a story about trust, because customers drawn to the name are being asked to trust the brand with their personal data.
'No Team To Handle This'
BYOD says it warned Trump Mobile about the intrusion before going public and was met with the line now drawing attention across the security world. The claim rests on the attackers' word alone, as the company has not publicly responded.
Researchers who examined the dump said it held names, email addresses, phone numbers, and pre-order details, along with records tied to Eric Brunnett, the Trump Organization's chief information officer. Despite the ransomware label, nothing published shows that systems were encrypted or that a ransom was demanded.
A Near-Unknown Gang, Not a Nation State
What makes the incident awkward is who carried it out. BYOD alleges it got in by infecting an employee at Liberty Mobile, a Florida firm tied to Trump Mobile's network, with malware before reaching exposed company subdomains. That is not the signature of an elite state-backed crew. It is the mark of opportunists walking through an open door.
A separate new group, EndZone, claimed in September that it had taken data on 4,000 users, though its claim was unverified. BYOD has denied any formal tie to EndZone.
Breaches Stretching Back to May
The trouble started well before either gang appeared. In May 2026, a website flaw exposed the personal details of roughly 27,000 people who had pre-ordered the company's gold-coloured T1 smartphone, which sells for $499 (£370).
An Australian IT expert found the hole with a simple web request and got no reply when trying to warn the company, and Columbia University professor Jonathan Soma reviewed the code. The leak was publicised by the YouTubers Coffeezilla and penguinz0. Trump Mobile confirmed that exposure, blamed a third-party platform, and said no financial data was taken.
What It Means for Trump Mobile Buyers
For anyone who handed over a name and address to lock in a pre-order, the question is whether that information is now circulating. Based on the leaked sample, the answer appears to be yes for thousands of them, and reporting indicates the dump even caught people whose signups failed.
The pattern also lands awkwardly for the brand's figurehead. In 2020, Donald Trump told a rally that 'nobody gets hacked' without 'somebody with 197 IQ'. Two unknown gangs and one coding error later, that line reads very differently.
© Copyright IBTimes 2026. All rights reserved.