

Trump Mobile Leak Exposes Its Own Security Chief as Hackers Claim Company Had 'No Team' To Handle Breach
Cybernews and other researchers said samples appeared legitimate, but Trump Mobile has not confirmed the breach or the attackers' claims
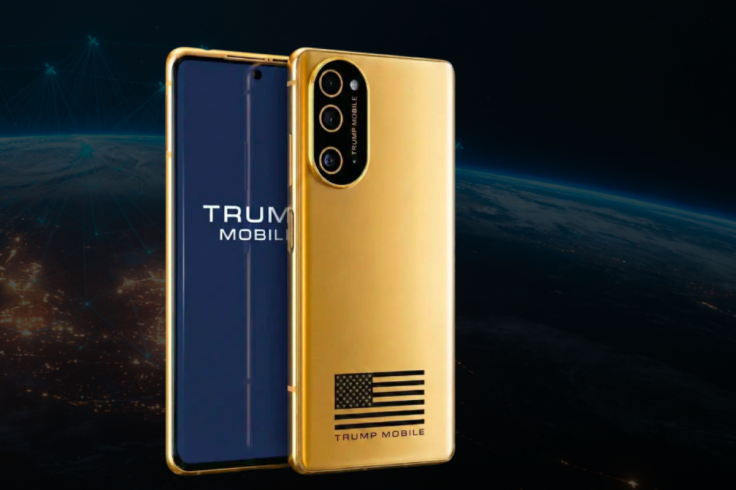
A hacking group claimed it stole the personal details of thousands of Trump Mobile customers, and the leaked data includes the name of the executive who oversees the Trump Organization's technology and information security.
The group, BYOD, claims to have taken data on 3,615 customers of the Trump-branded mobile phone service, including names, email addresses, phone numbers, home addresses and order details.
Researchers at Cybernews said on Tuesday 6 October 2026 that samples of the data appeared legitimate and were not linked to earlier breaches.
Trump Mobile has not publicly confirmed the breach, and the hackers' account of how it happened has not been independently verified.
The Trump Organization's Technology Chief
The most notable name in the dataset is Eric Brunnett, the Trump Organization's vice-president and chief information officer, Cybernews reported. His appearance in the customer records does not indicate that his own security was compromised beyond his details being listed.
Straight Arrow News first reported the leak on 5 October after reviewing the data and contacting people listed in it and described BYOD as a newly established group, found no Trump family members in the dataset.
Straight Arrow said it verified some of the entries by contacting people named in the data, which is the strongest independent check of the leak so far. That confirms individual records, not the full scope of what BYOD says it took.
‼️ We talked to the threat actor behind the Trump Mobile breach, who told us they infected a Liberty Mobile employee with an infostealer, got access to Trump Mobile through it and are still inside its systems.
— International Cyber Digest (@IntCyberDigest) October 5, 2026
Neither company was using any MFA, allegedly.
Turns out no security… https://t.co/KJH3rWwzZC pic.twitter.com/4iPtTjXojp
The dataset reaches beyond ordinary customers. International Cyber Digest, which also examined the leaked files, said the list includes several well-known names and people close to President Trump, Security Online reported. Their identities have not been published, and this article does not repeat any personal details from the leak.
The precise number is not entirely settled. The figure of 3,615 customers appears consistently across reports, though Cybernews also described the exposure as affecting almost 4,000 people.
A ransomware-tracking site lists BYOD's leak-site entry for Trump Mobile as having been posted on 29 September, about a week before the breach became widely reported.
'No Team To Handle This'
The most serious allegation concerns the company's response. BYOD says it warned Trump Mobile about the breach and was told the company had 'no team to handle this' and that 'anyone who hacks them is a terrorist'. That account comes from the attackers and has not been independently verified.
The group also claims continuing access. BYOD says it retains live access to a Trump Mobile backend dashboard and supplied a screenshot showing customer information, a claim that has not been confirmed. Reports describe BYOD as a ransomware group, but nothing published establishes that it encrypted company systems or made a confirmed extortion demand.
BYOD alleges it gained initial access through an employee at Liberty Mobile, a Florida-based company, whom it says it infected with malware before moving to exposed Trump Mobile subdomains to extract data.
Reports summarising the group's claims say the attack relied on credential-stealing malware and the absence of multi-factor authentication on the accounts it used. Neither company has confirmed that account.
Trump Mobile is operated by T1 Mobile, a Florida-registered company, using branding licensed from the Trump Organization, and its ultimate ownership has not been fully disclosed, according to the reports.
A Second Data Scare in Five Months
The latest allegations follow a separate data exposure in May, when Trump Mobile acknowledged that customers' names, email addresses, mailing addresses, phone numbers and order identifiers had been accessible through a third-party platform, TechCrunch reported at the time. A company spokesperson said then that it had found no evidence of a breach of its own network, systems or infrastructure.
Cybernews said its researchers found no link between the samples in the latest report and earlier breaches, and any connection between the two incidents has not been established.
The service has a short history. Trump Mobile was unveiled in June 2025 by Eric Trump and Donald Trump Jr. as a Trump-branded mobile virtual network operator, a carrier that resells access to existing networks rather than running its own, with a headline monthly plan priced at about £35 ($47.45). That model typically depends on partner companies for customer service, activation and other back-office functions, which is the kind of relationship BYOD says it exploited.
For customers, the practical risks follow from what was reportedly taken. Names, email addresses, phone numbers and home addresses are often used to make phishing messages more convincing, and for a mobile carrier's customers in particular, such details can be used in attempts to persuade a provider to transfer a phone number to a criminal's SIM card.
Customers are typically advised to add a PIN or passcode to their mobile account, enable multi-factor authentication where available and treat unexpected messages about their account with caution.
Trump Mobile had not publicly commented when the reports were published, leaving the scope of any unauthorised access and whether customer data remains exposed open.
© Copyright IBTimes 2026. All rights reserved.