

Building on Real-World Enterprise Experience: Inside Manoj Parasa's Research and Technical Contributions
The NexoVault concept combines workforce information, cyberattack monitoring and encryption to help organisations with limited security resources manage sensitive data
Modern businesses hold more sensitive information than ever before. Employee records, customer details, payment information, access credentials, and internal approvals now move constantly between cloud platforms, business applications, and connected databases.
Artificial intelligence can help organisations monitor this activity, but the challenge is not simply detecting something unusual. Companies must also determine whether the activity represents a genuine threat, protect the information involved, and understand the person and business purpose behind it.
Large corporations usually address these needs through separate cybersecurity, encryption, workforce-management, and monitoring products. They can afford several software subscriptions, dedicated security teams, and employees who manage the connections between those systems.
For a small or medium-sized business, the same model may be too expensive and difficult to maintain. Yet these companies hold sensitive information and face many of the same security risks.
Connecting Enterprise Experience with Research
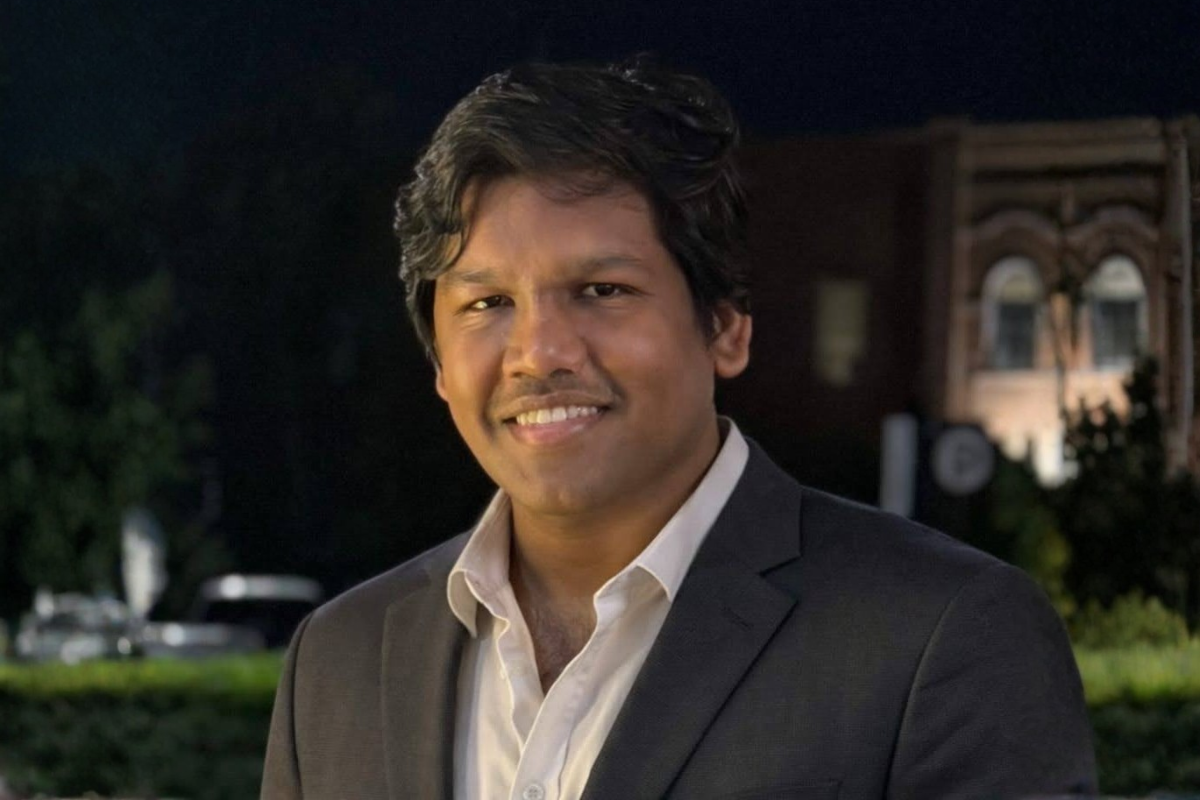
Manoj Parasa encountered this gap through more than a decade of work with enterprise workforce systems. He is a Senior SAP SuccessFactors Consultant at Ernst & Young, where his work involves platforms used by large organisations to manage employee records, roles, permissions, performance information, and other workforce operations.
That experience gave him a practical view of how enterprise information is organised and where security gaps can develop. A workforce system may show what an employee is responsible for, while a security product records what the employee did inside an application.
An encryption service may protect the information itself. Because these functions often operate separately, reviewing a single incident can require several teams to collect records from different places.
An alert may show that an employee opened a sensitive billing file, for example. By itself, that information does not establish whether the activity was improper.
A reviewer must also know whether the employee was assigned to the client, had the correct permission, was completing an approved task, and handled the information through a protected connection.
Parasa saw that this was not only a technical issue. It was also a question of cost, staffing, and day-to-day management. A global corporation may be able to operate three specialised products and employ teams to review them. A smaller company may have only a few people responsible for technology, security, and operations at the same time.
Rather than treating the problem only as part of his consulting work, Parasa began examining it through applied research.
His studies have covered artificial intelligence, machine learning, enterprise workforce systems, secure data exchange, access control, and cybersecurity. His publication record includes work available through Google Scholar, along with papers published through venues associated with IEEE and Springer.
A consistent question runs through much of this work: how can organisations use intelligent systems without separating security from the business context in which an event occurs?
Threat detection is more useful when it can distinguish between an employee completing an assigned task and someone accessing information without a valid reason. Encryption is more useful when it is applied automatically as information moves between systems.
Workforce information becomes more valuable when it explains who had access, what that person was expected to do, and whether the activity matched those responsibilities.
Instead of creating another stand-alone security dashboard, Parasa focused on connecting threat detection, data protection, and workforce information within one operating structure. The technical foundation of that work is reflected in three intellectual-property assets developed by Parasa and his collaborators.
The first, 'Data Processing Device for AI-Based Employee Management and Work Information Display,' concerns the connection between employees, their assigned responsibilities, and relevant work information. It provides a basis for placing technical activity alongside the role and assignment of the person involved.
The second, 'Computer Device for Cyberattack Detection,' addresses the identification of unusual system behaviour, including unexpected access attempts and activity that may indicate misuse or an external attack.
The third, 'AI-Powered Data Encryption Device,' concerns the protection of information while it is stored and while it moves between connected systems.
Although each intellectual-property work serves a different function, Parasa and his collaborators recognised that the functions become more useful when they operate together. That thinking led to NexoVault, a platform designed to connect workforce context, threat detection, and data protection within a single environment.
Designing for Companies with Limited Resources
The central idea behind NexoVault was shaped by the needs of organisations that cannot maintain several expensive security products and large specialist teams. The platform was designed to provide threat monitoring, encryption, and workforce context without requiring a company to replace its existing business applications.
Its security function monitors system activity and identifies behaviour that may require review. Its encryption function protects selected information while it is stored or transferred. Its workforce function connects the activity with details such as the employee's role, permissions, assignment, and current responsibilities.
Artificial intelligence is used to examine patterns and bring unusual events to the attention of reviewers. It can also support routine actions, such as applying protection to information or organising the details connected to an alert.
The aim is to reduce manual work, not to remove people from important decisions. A security or business professional still determines what the event means and what action should follow.
This structure is intended to give a smaller team one place to answer several related questions. What happened inside the system? Who was involved? Did that person have a valid business reason? Was the information protected? Does the event require further investigation?
For smaller organisations, that shared view can be more practical than moving between several dashboards and asking different departments to reconstruct the same event. It can also reduce the possibility that an important detail will be missed while information is transferred from one team to another.
Learning Directly from Smaller Organisations
Parasa's work did not remain limited to publications and technical concepts. He began engaging with smaller organisations, including Jhaishna Technologies, Studio M+N, and East World, to understand the security and operational problems they encountered in their own environments.
These discussions helped identify issues that may not appear in a research setting. Smaller companies often use a mixture of cloud applications, billing systems, customer-management platforms, and internal tools added at different stages of growth. Their access rules may also change quickly as employees move between projects or take responsibility for several functions.
Parasa and his team collected information about these operating challenges and used it to refine how the platform handled permissions, system connections, data formats, alerts, and employee assignments. The companies were not treated only as end users receiving a finished product. Their requirements helped shape how the technology was configured and tested.
This approach also revealed where automation was useful and where human review remained necessary. Routine monitoring and data protection could be handled with less manual effort, while questions involving employee intent, business approval, or unusual circumstances still required professional judgement.
Testing the Work Under Business Conditions
Pilot programmes allowed the technology to be tested with working business systems rather than only with sample information. The evaluations examined whether the platform could connect with existing applications, identify activity that required attention, protect sensitive information, and present the relevant workforce details in a form that teams could review.
The pilots also provided a practical measure of whether the technology saved time. A platform may perform well in a demonstration but still create more work if employees must repeatedly correct permissions, enter information by hand, or move between separate screens. The participating teams therefore considered not only whether the functions worked, but whether they made daily operations easier to manage.
As the testing progressed, Parasa worked with technical and operational teams to address differences in access models, integrations, and data structures. The tool was adjusted around the way each organisation already worked rather than requiring every business to follow one fixed setup.
After reviewing the pilot results, participating organisations began incorporating the relevant functions into their operating cycles. The value was practical: fewer disconnected checks, less time spent gathering context around an alert, improved visibility into access activity, and a clearer way to protect information as it moved between systems.
Research Measured Through Practical Use
Parasa's work illustrates the difference between describing an enterprise problem and building something that can operate within the limits of an actual business. His research provided the technical direction, the intellectual property established the protected foundations, and the pilot programmes tested whether those ideas could function alongside existing systems and small operational teams.
The result is not a claim that one platform can replace every specialised security product. Large organisations with complex infrastructure will continue to require dedicated tools and teams. The more focused contribution is a practical model for businesses that need stronger protection but cannot support several disconnected products and the staff required to manage them.
By bringing threat detection, encryption, and workforce information into one place, Parasa has concentrated on a part of enterprise security that is often overlooked: smaller organisations need effective protection too, but that protection must be affordable, understandable, and manageable with the people they already have.
His work continues to develop at the point where research and enterprise practice meet. That combination has allowed him to move from studying gaps in existing systems to building and testing technology intended to address them under real business conditions.
© Copyright IBTimes 2026. All rights reserved.