

Trump Mobile Data Leak Exposes Personal Details of Customers Who Never Even Finished Signing Up
A hacking group claims to have leaked the personal details of 3,615 Trump Mobile customers, raising fresh questions about the company's security and response
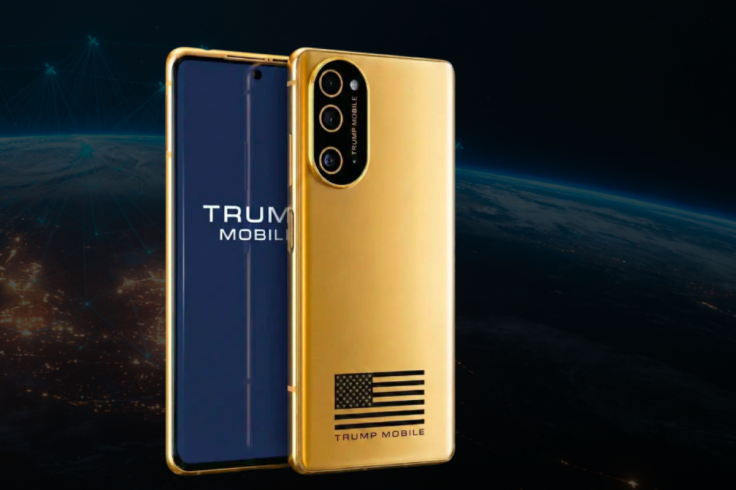
Trump Mobile customer records, including names, home addresses, phone numbers, email addresses and order histories for 3,615 people, have been posted online by a cybercrime group, potentially exposing even those who never finished signing up for the Trump‑branded service.
The data appeared on BYOD's dark web leak site in late September, according to Straight Arrow News, which reviewed the dataset and contacted people named in it.
The claim is the latest problem for Trump Mobile, the Trump‑branded wireless venture launched by Donald Trump Jr and Eric Trump. Neither Trump Mobile, the Trump Organization nor Liberty Mobile, the Florida‑based operator said to power the service, had responded to requests for comment at the time of reporting.
BYOD says it obtained the material after infecting a Liberty Mobile employee's device with malware. The group also claims it moved from that access point into exposed Trump Mobile subdomains and still had access to a customer dashboard, although that access has not been independently confirmed.
What the Trump Mobile Leak Contains
The published records appear to relate to Trump Mobile's wireless service rather than orders for its gold‑coloured T1 smartphone. BYOD said it took data on 3,615 people because that was the number using or previously using the carrier, according to PCMag.
Some entries reportedly concern people who never completed the sign‑up process. One person contacted by PCMag said they had not managed to set up an account but had still provided an email address and phone number, which suggests the exposure may extend beyond active customers.
The dataset also reportedly includes information connected to Eric Brunnett, the Trump Organization's vice‑president and chief information officer. Straight Arrow News identified his details in the leak, although the company has not publicly commented on that claim.
There is no indication so far that payment‑card data was included. That limits the immediate risk of direct card fraud, but the combination of names, addresses, phone numbers and order histories is still useful material for phishing messages pretending to come from a mobile network or delivery firm.
Hackers' Claim About Trump Mobile's Response
BYOD alleged that it warned Trump Mobile about the breach and received the reply, 'We have no team to handle this.' It also claimed the company described anyone who hacked it as a terrorist. Those statements come from the group's own leak‑site posting and have not been independently verified.
Security researchers have found reason to think the data itself is genuine. Straight Arrow News reached people who confirmed their details were accurate, while Cybernews said its samples looked authentic and did not match earlier breaches.
PCMag also contacted three people in the file, one of whom recognised an accurate record of cancelling a 30‑day unlimited plan.
BYOD may not be the only group claiming access. Another outfit, EndZone, said on 23 September that it had taken data on 4,000 Trump Mobile users. Security researcher Dominic Alvieri told The Register that the EndZone dump 'appears to be the same original breach', while BYOD denied a formal connection.
Why the Story Is Spreading
The leak spread quickly on X, where cybersecurity accounts highlighted the scale of the dump and the personal fields involved. One post from security researcher Abdulkadir, under the handle @cyber_razz, said Trump Mobile customers had had their data leaked and drew more than 7,800 likes, according to IBTimes UK's earlier reporting.
Other users were less interested in the technical details than in the customer count. Some questioned why the service appeared to have only about 3,600 wireless customers, while others mocked the company's security posture. Those posts reflect online sentiment rather than proof of the breach's mechanics.
Trump Mobile arrived with a high‑profile promise in June 2025, when Eric Trump said it would 'revolutionize cell phones'. Since then, the company has faced questions over its 'Made in America' claim, delayed shipping and revised preorder terms stating that 'a deposit is not a purchase'.
In January, lawmakers urged the Federal Trade Commission to examine the brand's marketing. The latest data‑leak claim adds a different kind of pressure, because it concerns not only what Trump Mobile promised customers but how it protects the information they handed over.
Trump Mobile has said nothing publicly about the BYOD claim. Until it does, customers who signed up, or merely began signing up, should treat unexpected messages about orders, refunds or account problems with suspicion.
© Copyright IBTimes 2026. All rights reserved.