

Massive DHS Data Breach Raises Fears for Undercover ICE Agents as Sensitive Operations Are Exposed
The archive reportedly contains contact details, job titles and internal access information
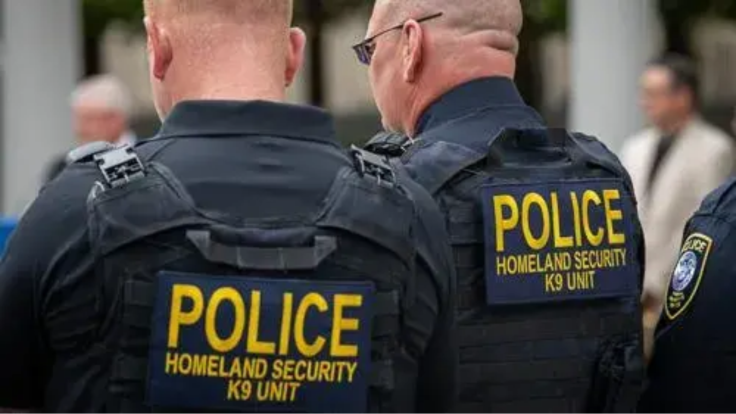
More than 41,000 US Department of Homeland Security (DHS) employees and contractors have reportedly had their professional details exposed in a major data leak, raising concerns about undercover Immigration and Customs Enforcement (ICE) personnel and sensitive surveillance operations.
The leaked records reportedly include contact information, job titles and internal access groups, potentially revealing how personnel and systems across multiple federal agencies are connected.
DHS Data Leak Exposes More Than 41,000 Workers
The archive, known as 'Icepick,' was published by the transparency organisation Distributed Denial of Secrets on 28 October. WIRED reported that the records cover DHS and seven component agencies, including ICE, US Customs and Border Protection (CBP), US Citizenship and Immigration Services and the Cybersecurity and Infrastructure Security Agency.
The information includes names, email addresses, telephone numbers, office locations, job titles and details about employees' supervisors and internal access groups. These records offer a broader picture of the department's organisational structure than a conventional staff directory, potentially exposing connections between personnel and the systems they use.
Reuters reported that it could not authenticate the entire dataset, although it corroborated some employee information through independent checks and direct contact with DHS staff.
Undercover ICE Agents and Surveillance Work Identified
WIRED's analysis found records associated with personnel involved in undercover operations, wiretaps and surveillance programmes. Some entries reportedly identify groups linked to investigative software, immigration databases and tools used to analyse telephone records and social media activity.
The dataset also reportedly includes personnel connected to Mobile Fortify, a facial-recognition application used by immigration agents, as well as accounts associated with encrypted messaging services.
The exposure of such information could create security risks if outsiders use it to identify personnel, impersonate officials or infer relationships between investigators and their operations. However, the publication of employee records does not automatically mean that active investigations have been compromised or that undercover identities have been conclusively exposed.
DHS Data Leak Raises Internal Security Concerns
The reported leak could provide insight into how DHS organises access to internal systems and distributes responsibilities among employees and contractors. According to WIRED, many records identify supervisors, while access groups reveal links between staff members and particular tools or programmes.
Alexander Leslie, a national security expert at Recorded Future, warned WIRED that the dataset could become more valuable when combined with other compromised information. Such cross-referencing could help malicious actors develop convincing impersonation attempts or identify vulnerable personnel.
The potential consequences therefore extend beyond the exposure of telephone numbers and email addresses. Information about professional relationships and access permissions could also help outsiders better understand the department's internal operations.
Homeland Security Responds To Reported Data Leak
DHS acknowledged a potential breach and said it was working to address the situation and protect employees, according to Reuters. The department also said it would provide further information when more details became available.
The circumstances surrounding the alleged breach remain disputed. Distributed Denial of Secrets said the records were obtained from an entity calling itself the Department of Peace, which claimed responsibility for the disclosure. The organisation said the release was intended to promote accountability and support public scrutiny of government activities.
The group claimed the information originated from DHS' Okta sign-on service. However, Reuters could not independently verify that account. Okta said it had no evidence that its systems or data had been compromised.
The full extent of the exposure, including whether any active investigations or undercover operations have been affected, remains unclear.
© Copyright IBTimes 2026. All rights reserved.